←
All posts
Architecture
How Celestial Auth Is Designed
The IDP/PDP split, the Auth Switch, and an async provisioning problem I have not fully solved.
May 7, 2026 · 6 min read
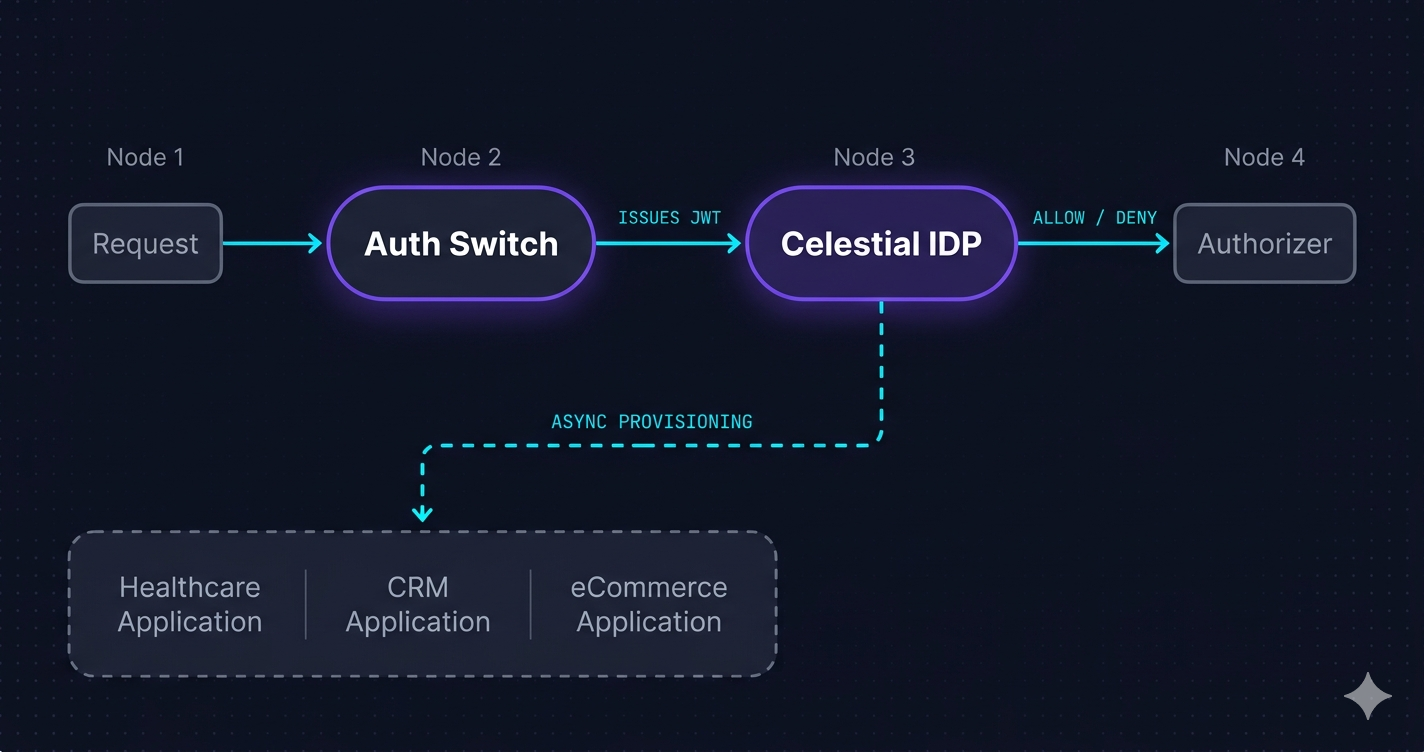
The IDP/PDP split
The **Identity Provider (IDP)** answers: who is this? It handles credentials and token issuance. The **Policy Decision Point (PDP)** answers: is this user allowed to do this thing, in this tenant, right now?
Why split them? Because they change at different rates. Credential logic changes with new auth methods (passkeys, magic links), while policy logic changes with product permissions. Mixing them means every credential change risks breaking authorization.
The Auth Switch and async provisioning
The **Auth Switch** is a routing layer that decides which flow a login attempt should use. This is where an unsolved problem lives: **async provisioning**. When a user authenticates via SAML for the first time, they are verified but no record exists in Celestial's user store. Right now, Celestial uses an event-driven approach with a short polling loop. It works, but it creates a visible pause for the user.